The Single Source of Truth for Vendor Reality
Right now, vendors have access to your data and systems. When one of them is compromised, so are you.
Hero maps those vendors with shadow access, including the ones that bypass security and procurement, and gives you one definitive record of third-party risk from first signal to final revocation.
The Full Vendor Lifecycle
Taking back control starts with seeing what's actually there. Legacy TPRM is list-first: it reviews what it was handed. Hero is reality-first: it discovers what's actually connected, follows what it does, and closes the gap between what you approved and what has access, automating the heavy lifting of third-party security at enterprise scale.
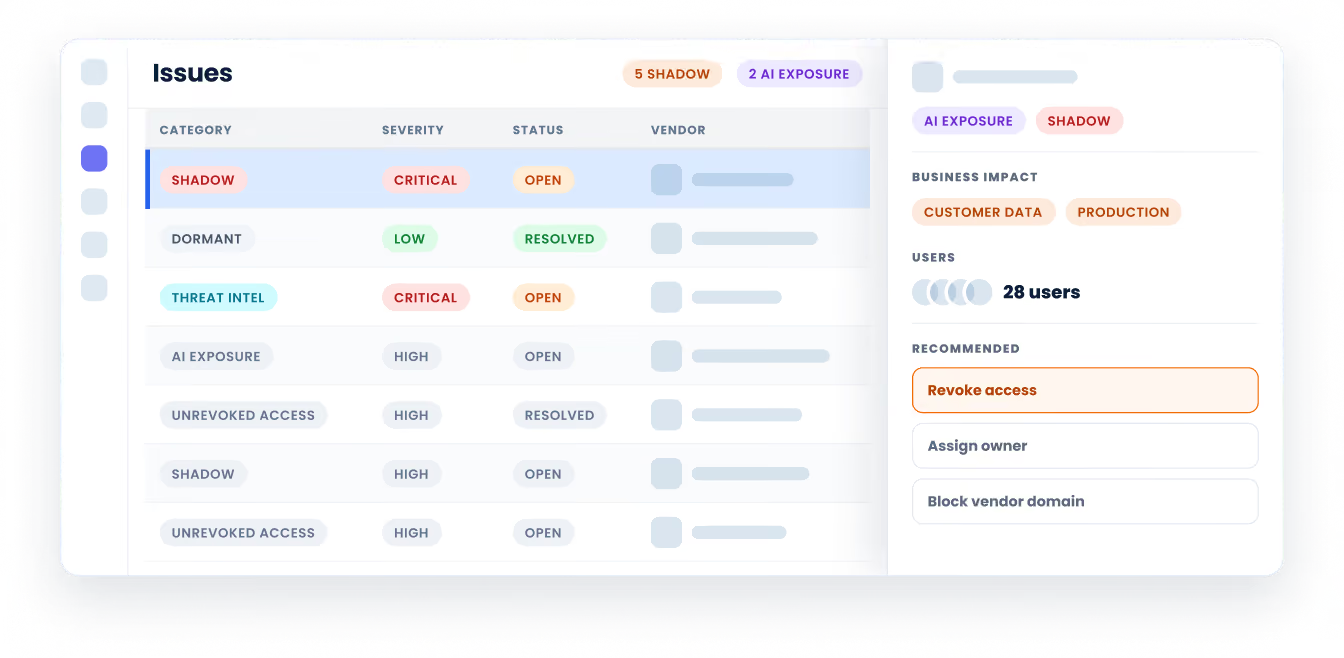
Surface every vendor with active access from observed signals across identity, communication and business records. Hero finds the shadow AI and forgotten integrations that bypass traditional intake.
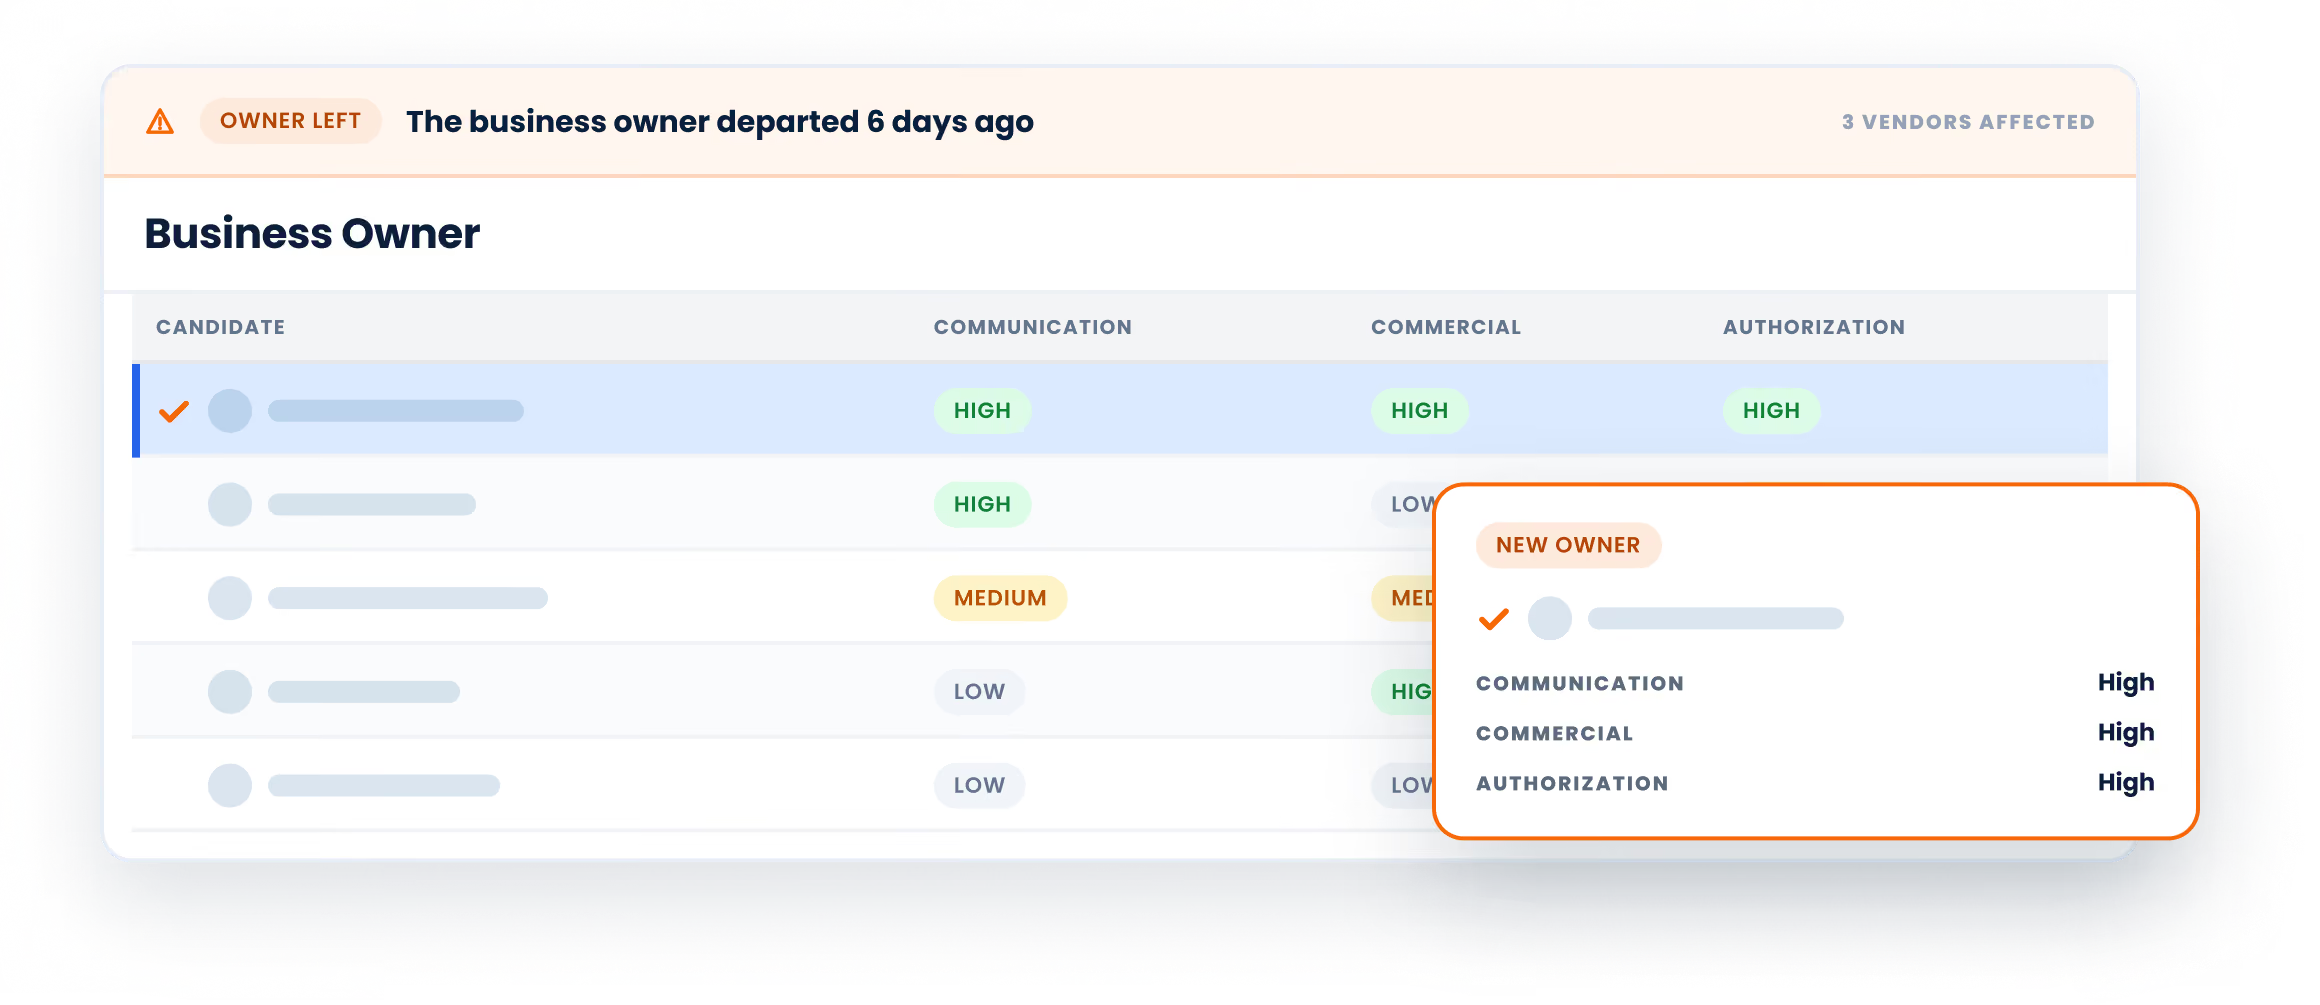
Determine business ownership, funding, and behavioral risk without a single questionnaire. Hero correlates technical reality with business intent to isolate the vendors that actually matter.
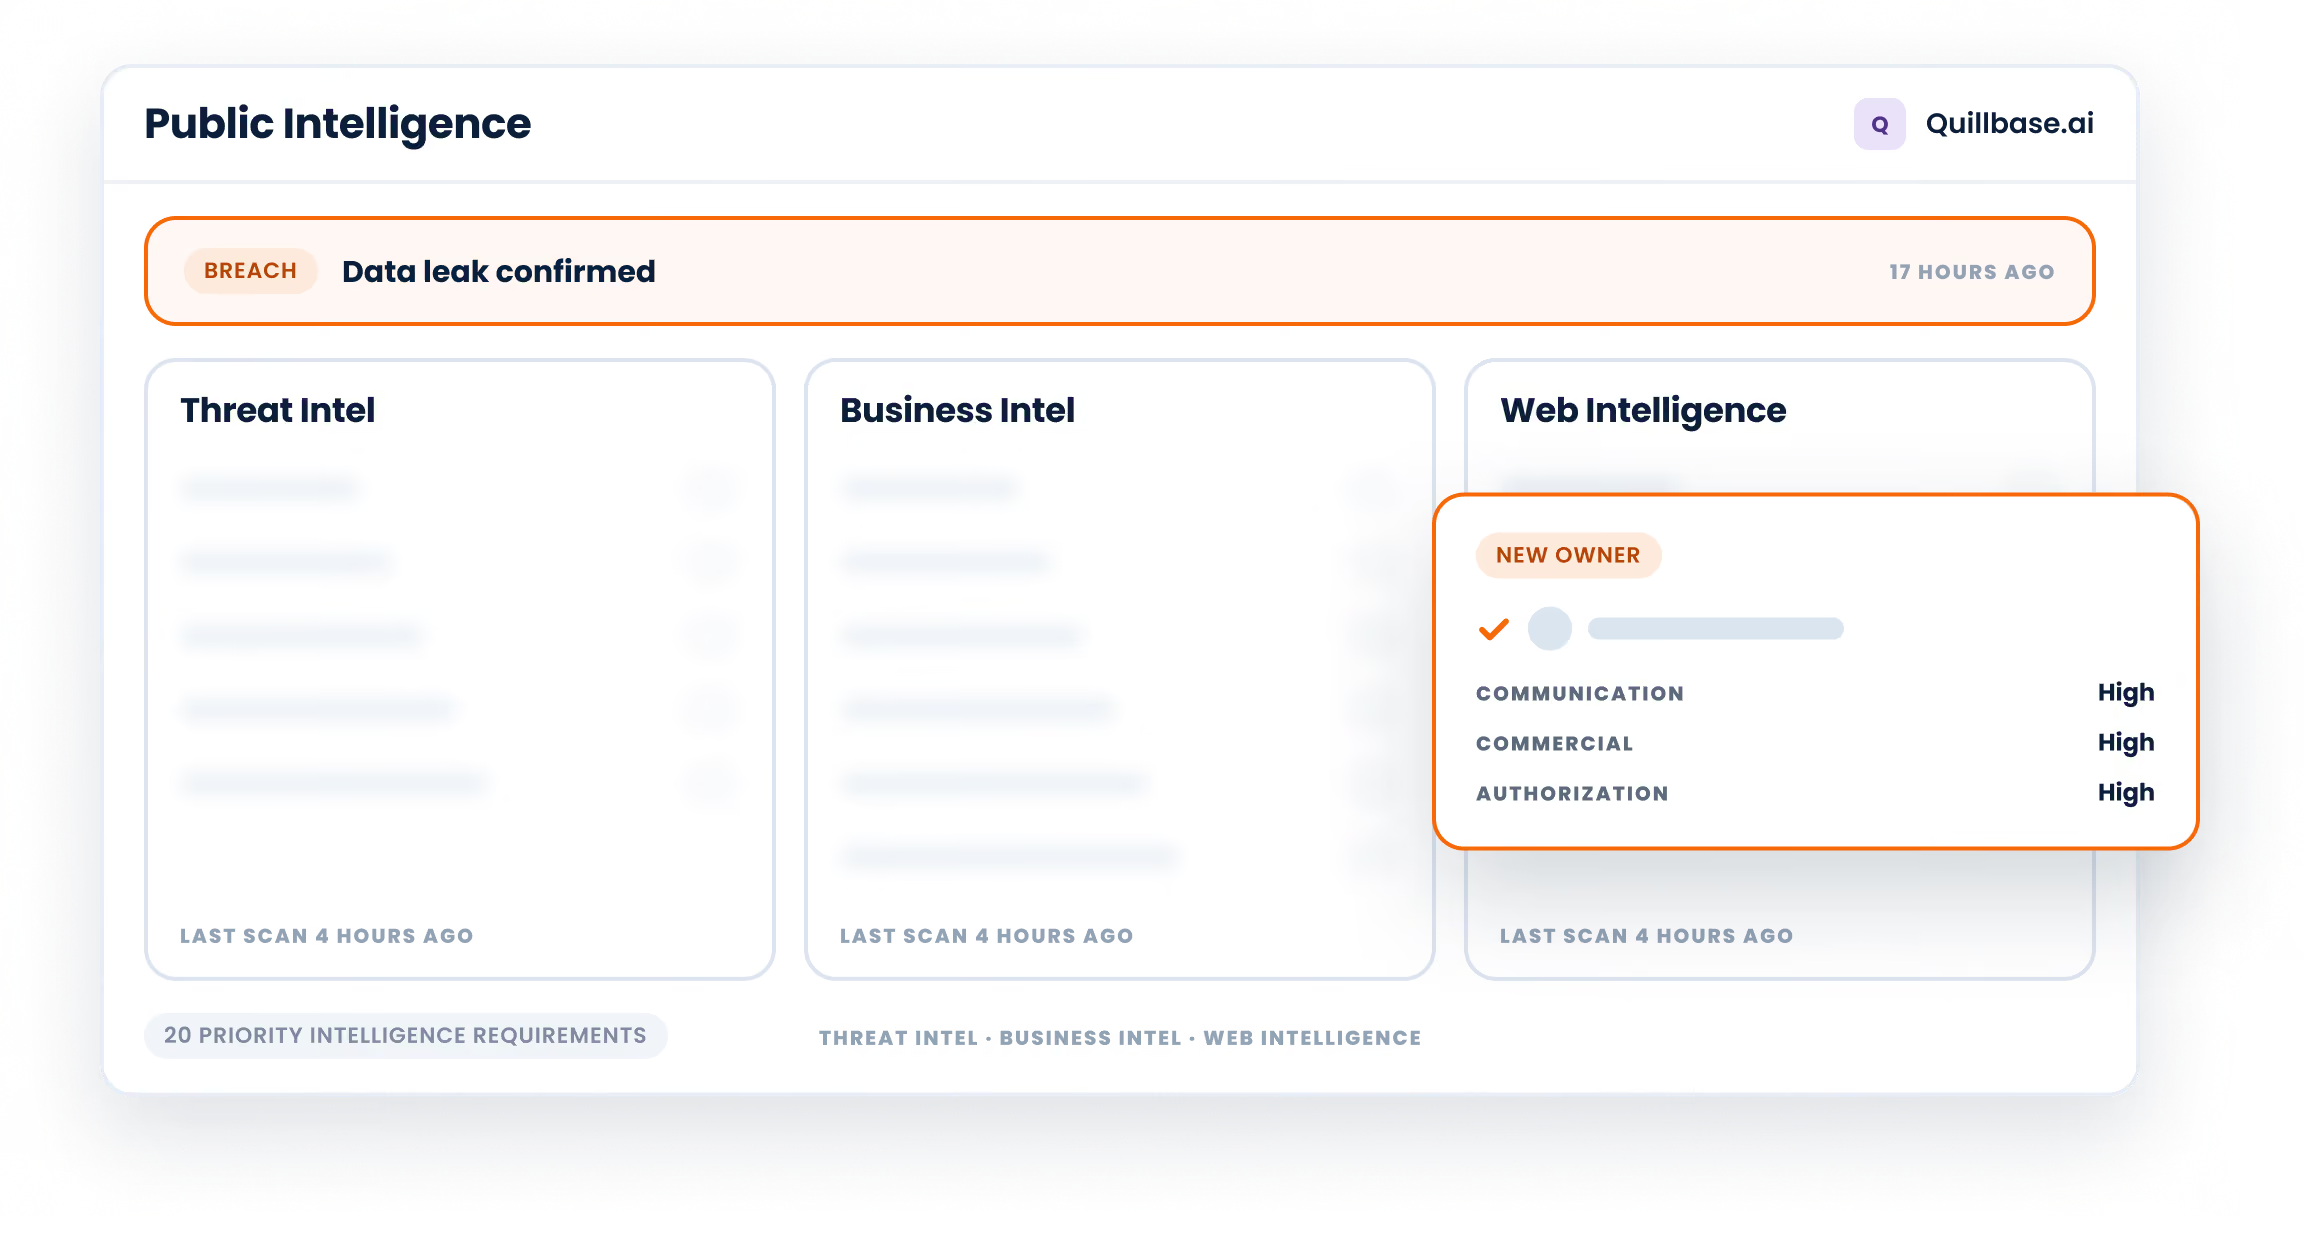
A breach only matters if the vendor has access to you. Hero correlates external breach signals, known vulnerabilities, and exposure against your live access map, so a compromised vendor surfaces against your real footprint, not as one more score. You see which relationships are actually exposed while it still matters.
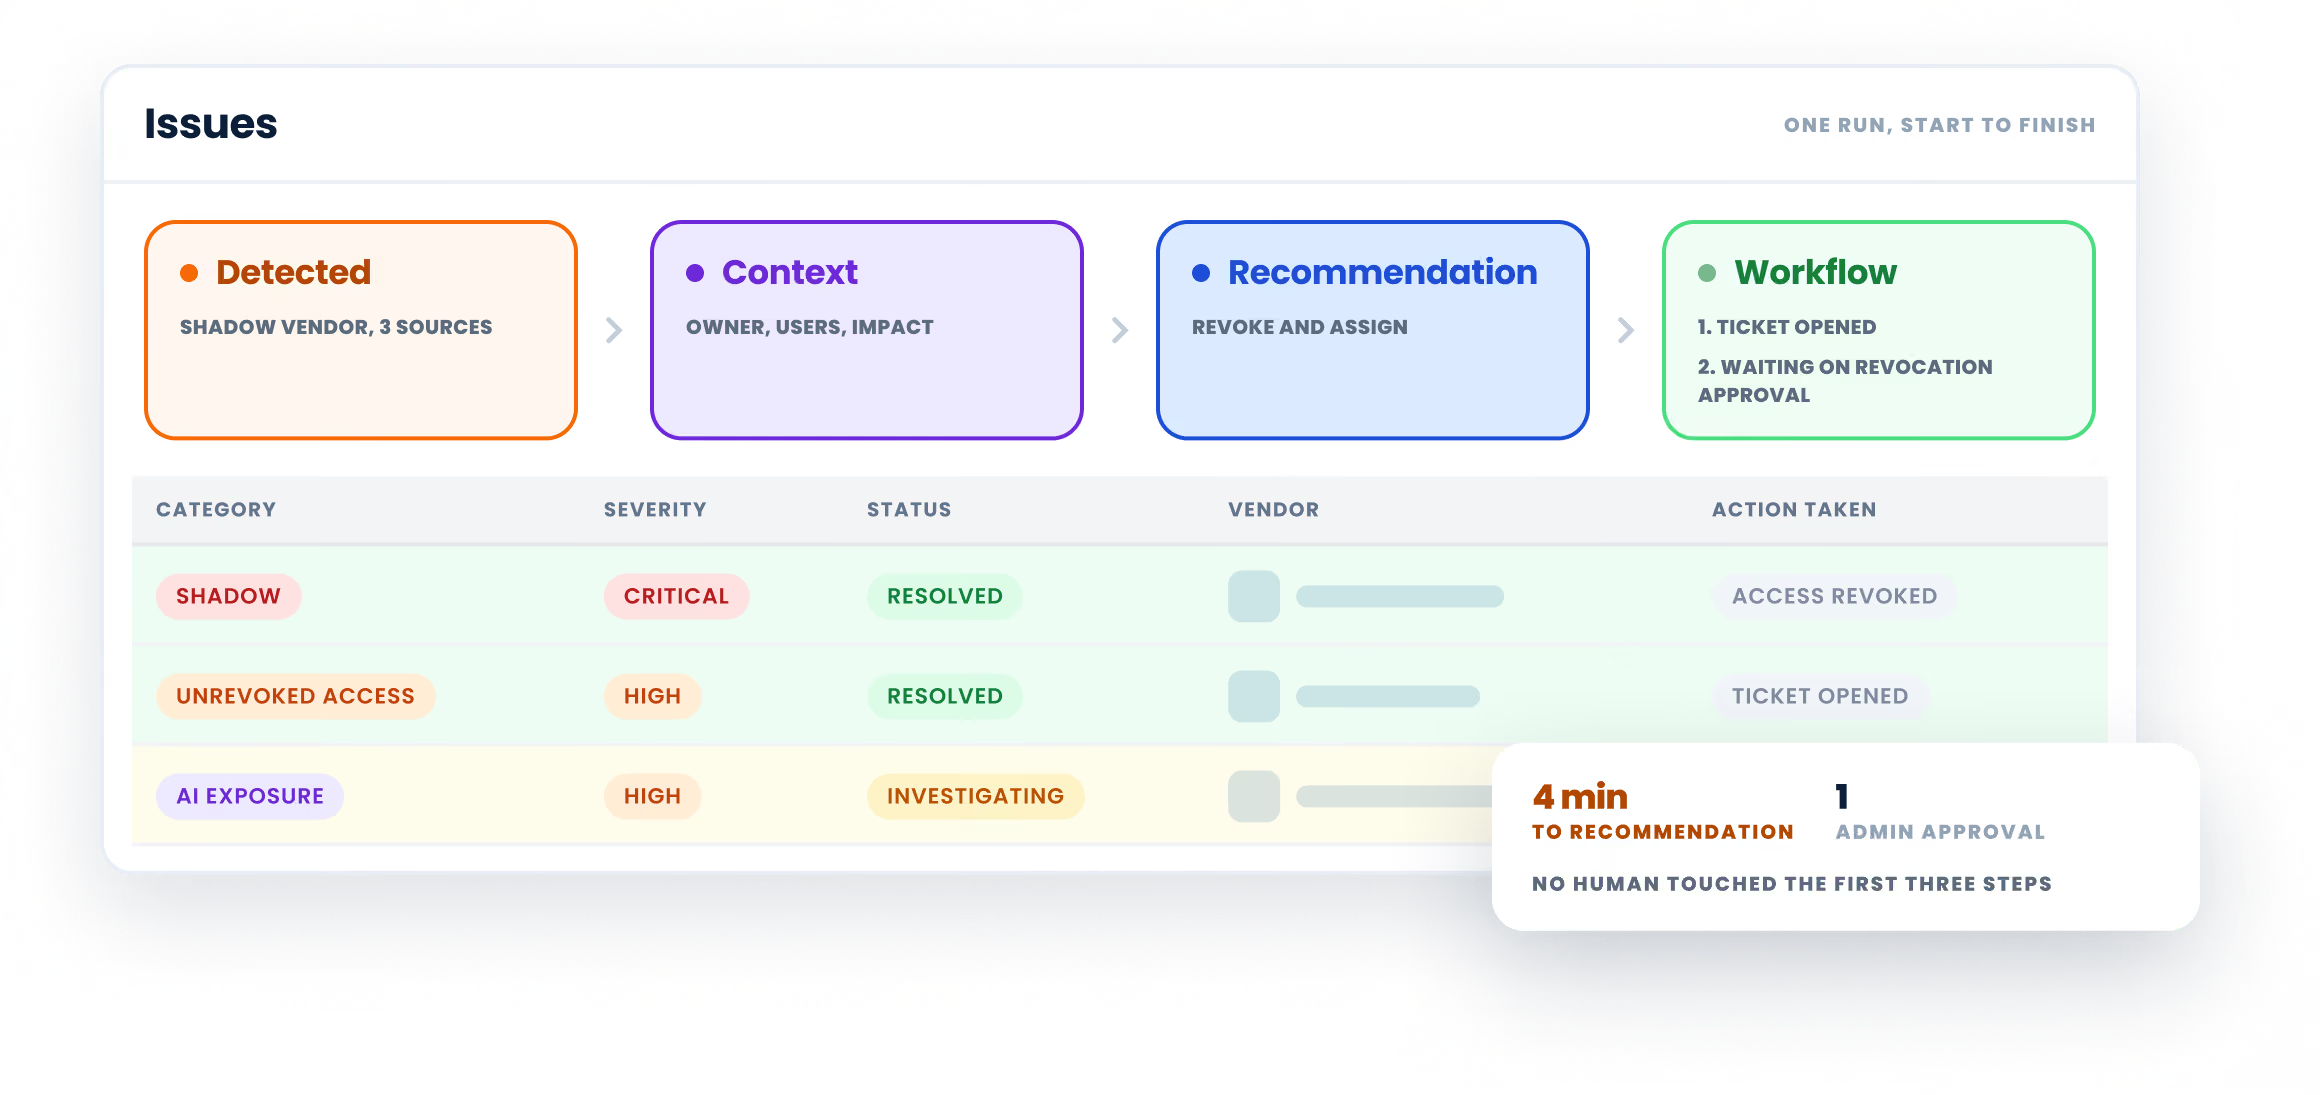
Close the loop. When access is stale, unrevoked, or unauthorized, Hero drives recertification and revocation directly in your existing tools to ensure access is cut, not just flagged.
Proactive Defense for the AI Era
Claude, Manus and OpenAI reading company data before anyone reviews them.
A team’s free trial that never reached procurement.
Access that outlives the contract. Non-Employee Identities
Standing permissions no one explicitly granted.
Hero surfaces each one from signals already in your stack: email, procurement, identity, network. No questionnaire, no list to maintain



A breach only matters if the vendor still has access to your environment.
Hero correlates breach signals, known vulnerabilities, and real exposure directly against your active access map. While discovery identifies what holds access and threat intel highlights what is exploitable, Hero delivers actionable exploit paths instead of endless security scores. You immediately see which vendor requires remediation first, whether access remains active, who owns the relationship, and what assets are reachable.
Contractors, consultants, and agency staff get access to your systems without Security ever provisioning it - a login shared by the team they work with, an invite to a tool, an admin permission granted in the moment. Security often doesn't know the access exists, so when the engagement ends, no one shuts it down. Hero discovers every non-employee with active access from the signals already in your environment, tracks what they actually touch, and drives revocation when the work is done, whether or not anyone logged them in the first place.
When access becomes stale, unowned, or unauthorized, Hero goes beyond simply logging a ticket. It actively automates recertification and revocation through your team's existing tools, ensuring access is fully terminated rather than merely flagged.
Beyond legacy lists & external generic scoring
List-driven solutions only evaluate submitted vendors, and outside-in rating tools score third parties from a distance regardless of actual connectivity. Hero focuses on active access, identifies true exploitability, and neutralizes the threat.
Discovery-First Architecture
Exposes coverage gaps automatically without needing manual audits.
Designed for the AI Era
Treats AI vendors, autonomous agents, and non-employee entities as primary risk types.
Full-Lifecycle Control
From first signal tofinal revocation
About the Team
We’ve worked in cybersecurity and AI for most of our careers, much of it looking at systems the way an attacker would. One problem kept coming up: companies had a vendor list, but the real number of vendors with access to their systems was always higher, and nobody was tracking the difference.
We started Hero to close that gap. It finds every vendor connected to your systems, including AI tools, SaaS apps, contractors and integrations, and keeps that picture current, so security teams can say yes to new tools without losing track of who has access.
Vendor security has spent a decade getting better at managing the list,
It's time to secure vendor reality.
FAQs
- How is Hero different from a traditional TPRM tool?
- Do our vendors need to fill out a questionnaire?
- How does Hero find shadow AI and unauthorized tools?
- Does Hero work with our existing identity and ticketing tools?
- How is access actually revoked?
- How long until we see our actual vendor footprint?